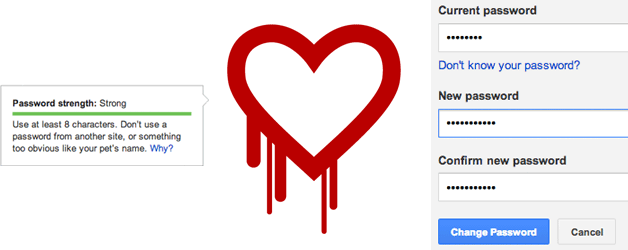
The price of online security? Eternal vigilance!
April 11, 2014On Monday 7 April 2014, a widespread issue in a central component of Internet security was disclosed.
Registered in the Common Vulnerabilities and Exposures system as CVE-2014-0160, the vulnerable code, called ‘Heartbleed’, had been adopted for widespread use upon the release of OpenSSL version 1.0.1 on March 14, 2012.
The vulnerability, could allow attackers to gain access to privileged information on any site running a vulnerable version of that software. The vulnerable versions were OpenSSL 1.0.2-beta and OpenSSL 1.0.1 – OpenSSL 1.0.1f.
Conduct an online test of your server/s
On 10 April 2014, The Huffington Post reported that “Cisco Systems and Juniper Networks, two of the biggest creators of Internet equipment, announced that their products had been affected by the Heartbleed bug. Routers, firewalls and switches … have all likely been affected by the bug, leaving your personal information at risk of being stolen by hackers.”
Another Huffington Post article explained: “Every time you log into a website, your login credentials are sent to that website’s server. But in most cases those credentials aren’t simply sent to the server in plain text — they’re encrypted using a protocol called Secure Sockets Layer, or SSL. As with most protocols, different software makers have created different implementations of SSL. One of the most popular is an open-source implementation called OpenSSL, used by an estimated two thirds of currently active websites.”
“Heartbleed is a bug in OpenSSL. Hackers can exploit Heartbleed to get raw text from emails, instant messages, passwords, even business documents — anything a user sends to a vulnerable site’s server.”
The article continued in an ominous tone: “And the scariest part? The Heartbleed security flaw existed for nearly two years before it was discovered,” by ‘white-hat’ researchers.
Respected authorities deemed Heartbleed ‘catastrophic’. Forbes cybersecurity columnist Joseph Steinberg described the bug as potentially “the worst vulnerability found (at least in terms of its potential impact) since commercial traffic began to flow on the Internet”.
A fixed version of OpenSSL was released on April 7, 2014, (at the same time as Heartbleed was publicly disclosed). By that time, around half a million (approximately 17%) of the Internet’s secure web servers certified by trusted authorities, were believed to be vulnerable to the attack, allowing for the potential theft of the servers’ private keys and users’ session cookies and passwords.
After Digital Tsunami became aware of the issue, we checked that our private clouds were running non-vulnerable or patched versions of the Open SSL software. As intercepted security logins could potentially enable hackers access to databases, it is advisable to update passwords on any potentially vulnerable site. By changing a password on a site which may have been vulnerable between 2011 and this month, when servers began using the updated patched version of the OpenSSL software, removes the potential risk.
We strongly recommend regularly changing passwords as a standard precautionary measure. Although this current vulnerability was massive, there is limited information on particular sites which may have been targeted, but all users need to be constantly vigilant in the face of dedicated ‘black hat’ hackers and unknown risks.
Read about the most contagious malware released at the turn of the century.
Even though an outbreak on the scale of The Love Bug or the Melissa virus has not recurred, the potential has not diminished. In many ways it has increased, as malware is far more covert, polymorphic (an encrypted combination of trojan, mutating virus and bot), which is able to constantly modify itself to avoid detection or eradication.
In this case, the risk was not malware, but a vulnerability present in the very core of webserver security technology. Many respected sites using Open SSL were potentially vulnerable.
Now that all will have upgraded to the latest version of Open SSL, it is a extremely sensible security precaution to change passwords on any sites that you use as a corporation or individual, including:
- Amazon Web Services
- Dropbox
- Go Daddy
- GMail
- SoundCloud
- WikiMedia
- WordPress
- Yahoo
- YahooMail
- YouTube
All users should implement the highest level of security, including no less than: individual high-security passwords in a combination of at least 8 (preferably 12 or more) characters, containing at least one lower case character, one capital, one numeral and where accepted, special characters (such as ^+>&*#/%). These should not be formatted to resemble or contain a word and should not be used across all sites. It is exceptionally important that passwords for banking sites not be shared.
If your bank is not yet using two-factor authentication, comprised of a username and password PLUS a ‘token’ (random code generator device) or code sent to your to cellphone, it is time to consider changing banks!
Company and domestic networks, WiFi hubs, and webservers should all be protected with a firewall, anti-spam and anti-virus software, and regular scans to detect unwanted cookies or malicious threats. Using a reputable software, these threats should be quarantined and eliminated.
At least one backup generic email address (Gmail, Hotmail, Yahoo, etc.) should be created, to enable communications in case your domain name becomes infected and email on that domain is blocked or unusable. This email can also be used to retrieve passwords for an email account on your corporate domain.
Digital Tsunami constantly monitors and audits the security of our clients and our private clouds. Only a few days prior to the global awareness of the Heartbleed Open SSL vulnerability, we had conducted yet another security audit, to ensure that we were taking every possible measure to protect our clients’ assets.
Read about some of the security measures Digital Tsunami applies to web hosting and specifically to WordPress site hosting. (For security reasons, some details are deliberately vague and brands / softwares are unspecified).
Talk to Digital Tsunami about security for your web hosting.
References:
http://heartbleed.com
https://filippo.io/Heartbleed/ online Heartbleed tester
http://techcrunch.com/2014/04/07/massive-security-bug-in-openssl-could-effect-a-huge-chunk-of-the-internet/
http://mashable.com/2014/04/09/heartbleed-bug-websites-affected/
http://tif.mcafee.com/heartbleedtest
http://blogs.mcafee.com/consumer/what-is-heartbleed
http://en.wikipedia.org/wiki/Heartbleed
http://www.huffingtonpost.com/2014/04/08/heartbleed-66-percent_n_5112793.html
http://www.huffingtonpost.com/2014/04/11/heartbleed-routers_n_5132306.html
http://www.smh.com.au/digital-life/consumer-security/coles-mastercard-myer-visa-card-and-other-ge-money-partners-stung-by-heartbleed
http://en.wikipedia.org/wiki/Multi-factor_authentication
Recommended security vendors:
From Our Clients


Digital Tsunami provided an outstanding service throughout the whole web development process. Andrew spent extensive time early on to understand our business in order to provide additional conceptual and strategic contributions to the brand and corporate identity of Kinetic Defence Services to ensure the message was clear, precise and appealing to the target audience.
The development process was smooth and efficient and enabled us to have an input throughout to guarantee total satisfaction with the final look and feel of the site.
The launch .. was a success. We were able to present this live on a Wireless connection during our Sydney, Australia sales conference on a location with very limited internet bandwidth. This proves the technology used .. renders light webpages which are easy to download on a browser.
Comments I've heard from our employees were all positive and reflected precisely what we were looking for: a simple but concise, clean and effective webpage.
We acknowledge the timeframe given to you was extremely short but nevertheless you have sucessfully delivered the project on schedule .. the critical success factor was communication and availability of Digital Tsunami's team.
I am very glad we were able to partner with such a professional team as yours and I am confident any other initiatives with you will be as successful.
Since 2003, Digital Tsunami has collaborated with Personal Broadband Australia to deliver many online solutions, including the latest www.pba.com.au site.
Central to the development process is Digital Tsunami's thorough understanding of the project needs, clear and constant communication, and creative, innovative and meticulous approach to delivering solutions.
The results are clean, intuitive, refined and cohesive, with rapidly loading pages and extremely high usability.
The benefit to PBA of this long-term relationship has been the highly effective way in which Digital Tsunami has implemented and enhanced my vision on every project.
Andrew and his team have provided consistently good service and met both our needs and expectations. He certainly knows his stuff and delivers workable web solutions in a highly professional manner.

.. a reliable and steadfast operator, with a keen sense of service. Innovative and contemporary, and operating within the upper echelon.